

Microsoft Patch Tuesday, October 2026 Security Update Review

Table of Contents
- Adobe Patch for October 2026
- Zero-day Vulnerabilities Patched in September Patch Tuesday Edition
- Critical Severity Vulnerabilities Patched in September Patch Tuesday Edition
- Other Microsoft Vulnerability Highlights
- Microsoft Release Summary
- Discover and Prioritize Vulnerabilities inVulnerability Management, Detection & Response (VMDR)
- Rapid Response withTruRisk Eliminate
- Qualys Monthly Webinar Series
Microsoft has released its October 2026 Patch Tuesday security updates, addressing vulnerabilities across its products and services. As organizations continue to navigate an evolving threat landscape, applying security patches promptly remains critical to reducing exposure and strengthening security posture. This month’s updates highlight the importance of identifying affected assets, prioritizing remediation, and staying ahead of emerging risks.
This Patch Tuesday is Microsoft’s largest security update ever, marking a significant increase over other recent massive releases, including the 400 security fixes in August and over 970 in September.
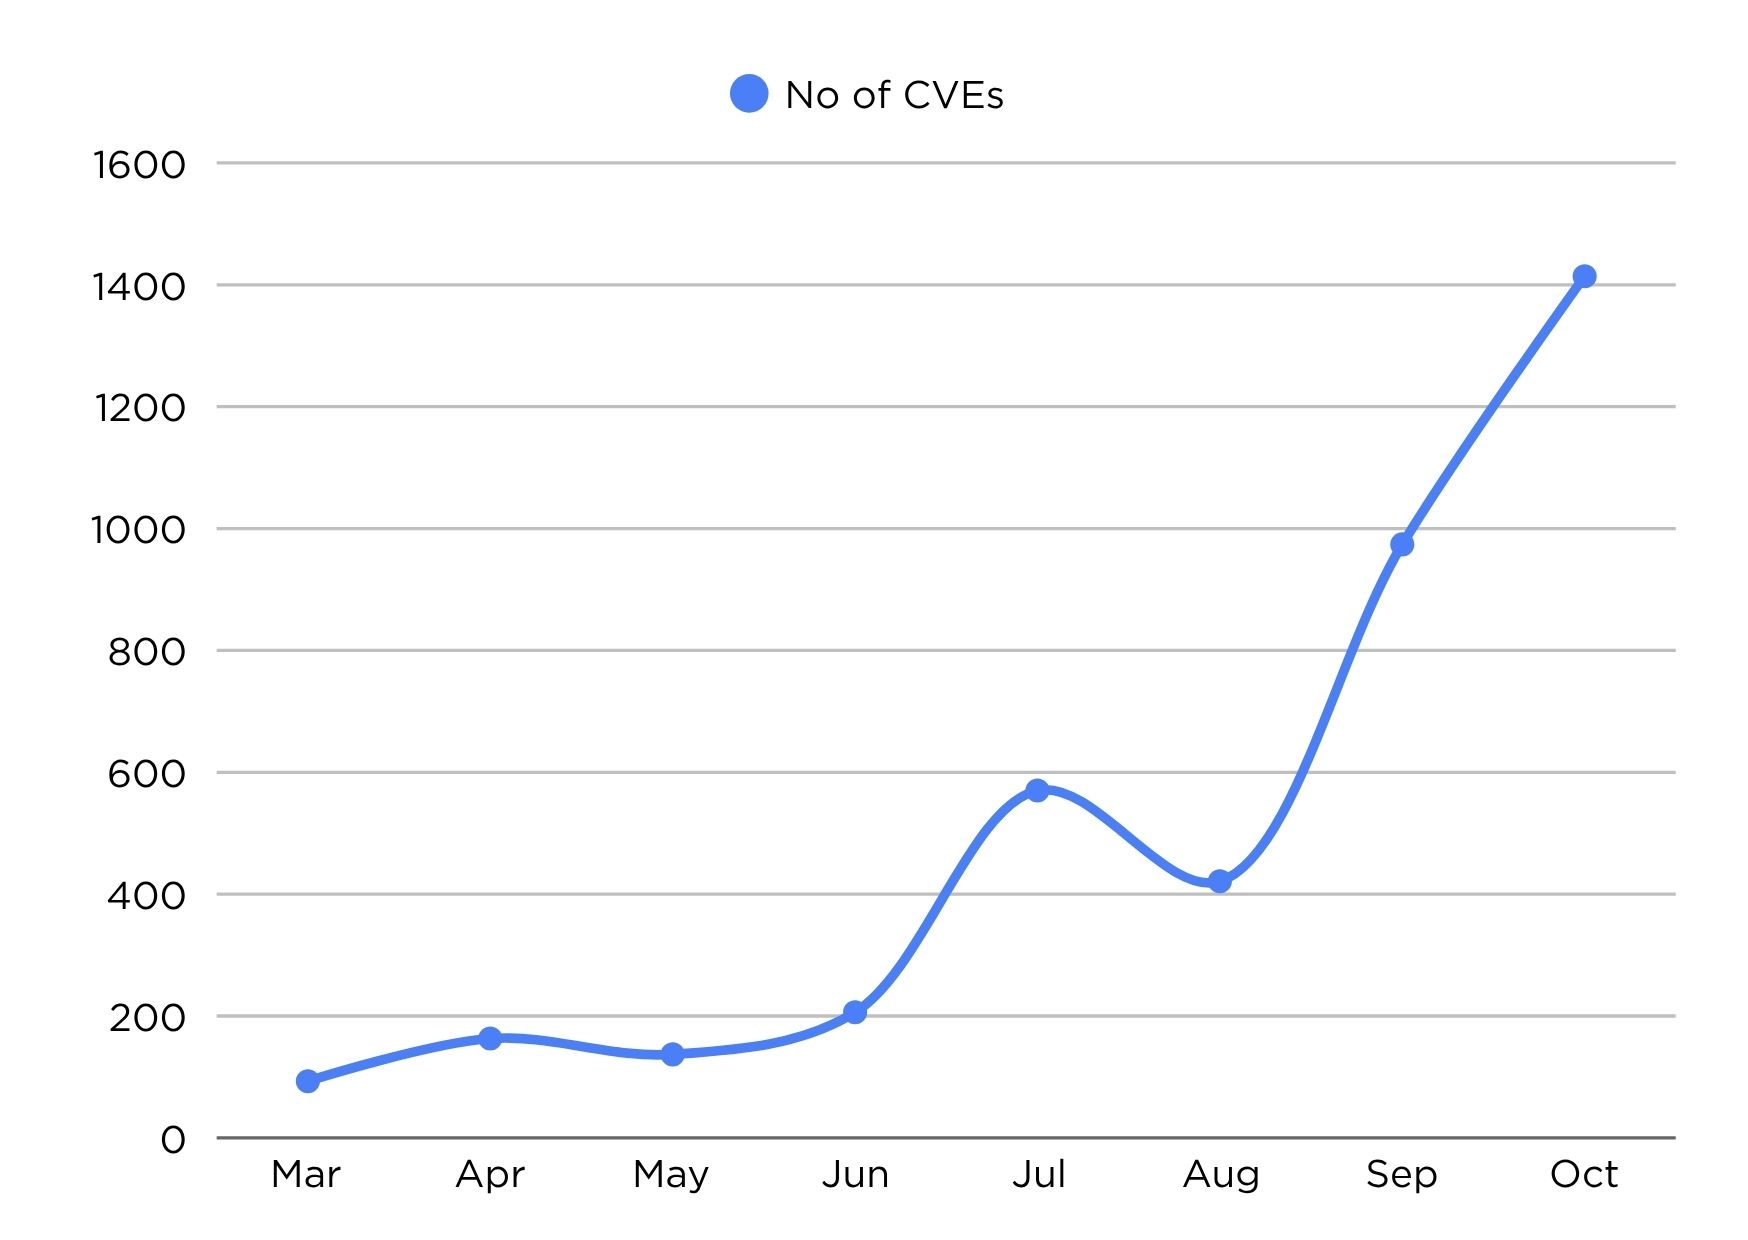
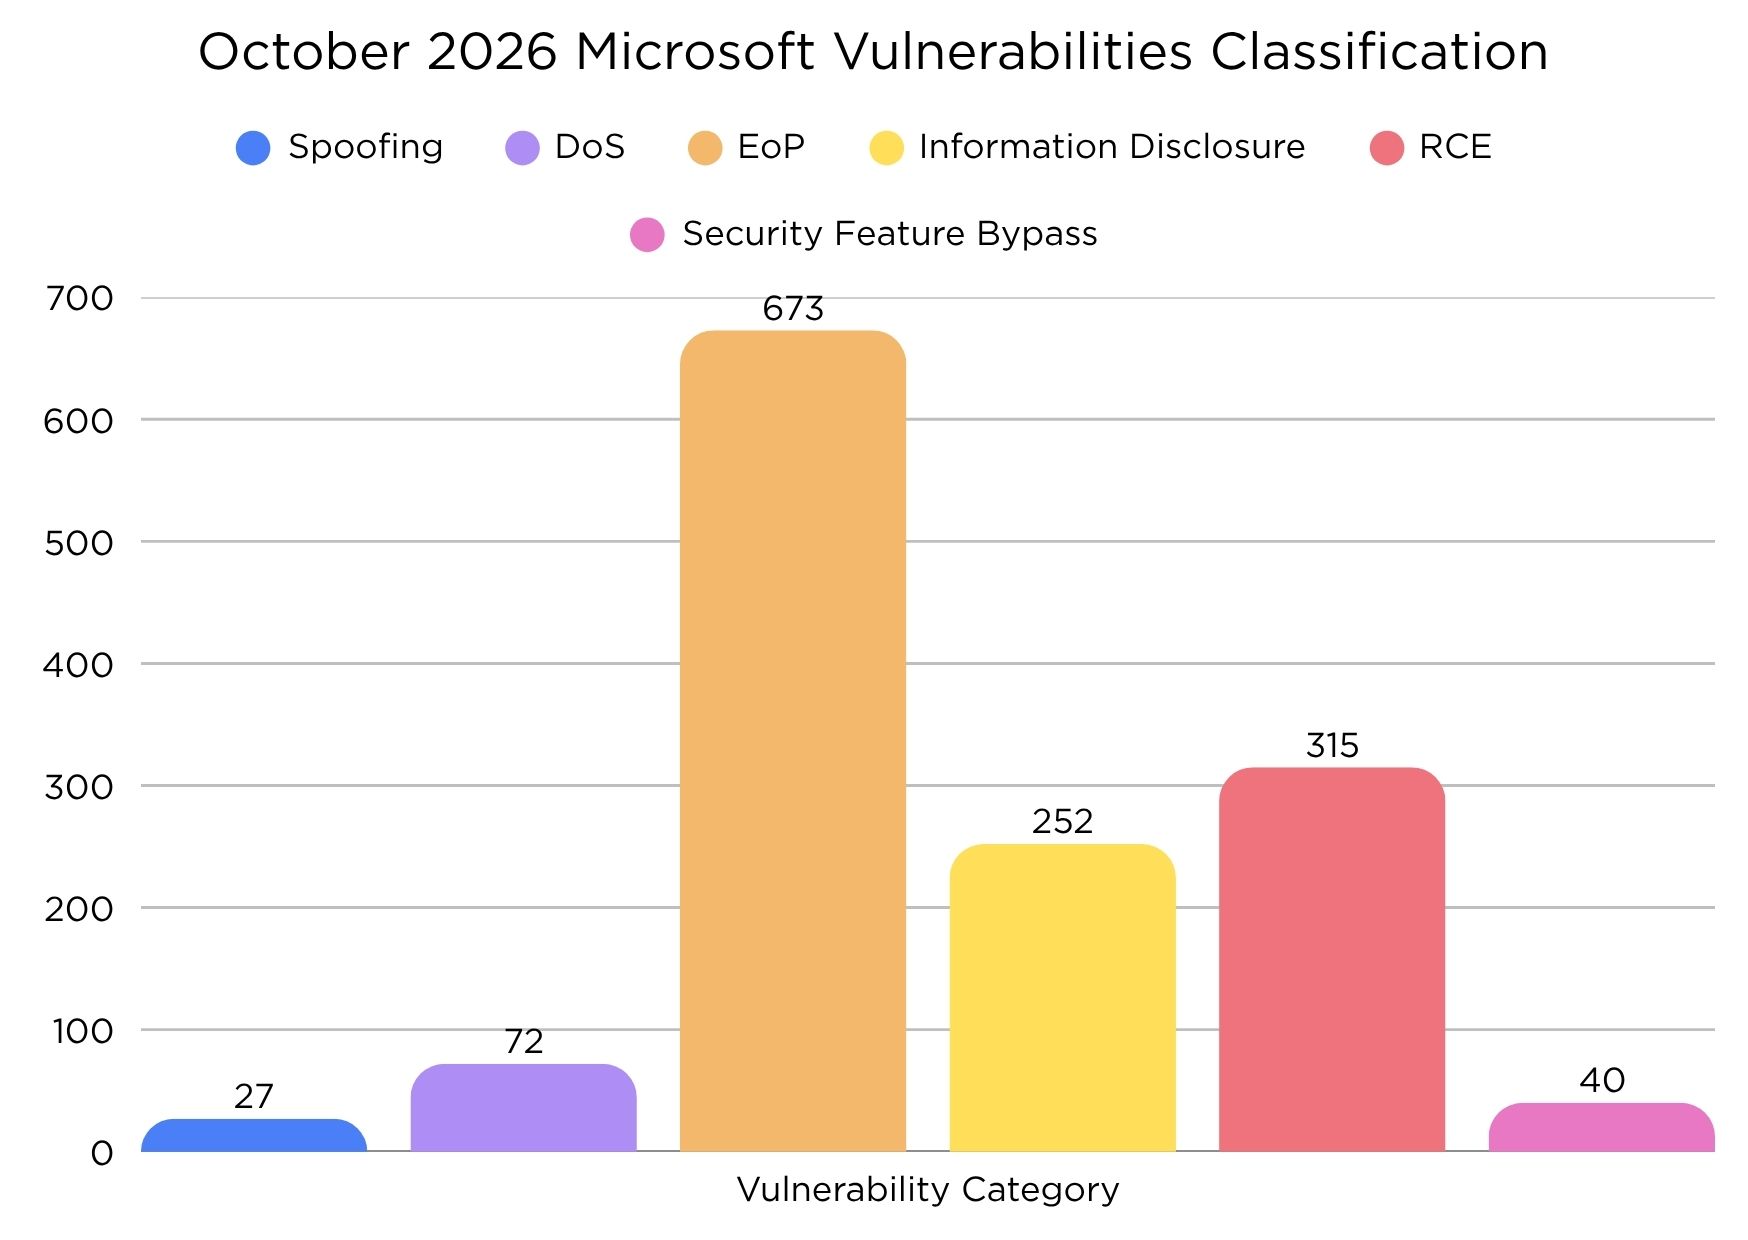
This month’s release addresses 1414 vulnerabilities, including 78 critical and 1329 important-severity vulnerabilities.
In this month’s updates, Microsoft has addressed two vulnerabilities, one of which has been exploited in the wild.
This month’s release includes fixes for several vulnerabilities that could potentially enable remote code execution, privilege escalation, or denial-of-service attacks. As always, timely patch deployment is crucial to reduce exposure and ensure systems remain resilient against exploitation attempts.
InstaScan delivers detections within 60 minutes. After October’s Patch Tuesday, Agent Insta customers had them within 5 minutes.
The October 2026 Microsoft vulnerabilities are classified as follows:
Adobe Patch for October 2026
Adobe has released 11 advisories addressing 176 vulnerabilities across Adobe Experience Manager, Adobe ColdFusion, Adobe Commerce, Content Credentials SDK, Adobe Dimension, Adobe Photoshop, Adobe Substance 3D Stager, Adobe FrameMaker, Adobe Substance 3D Designer, Adobe Substance 3D Sampler, and Adobe Bridge. 23 of these vulnerabilities are rated critical. Successful exploitation of these vulnerabilities may lead to privilege escalation, arbitrary code execution, and bypassing security features.
Zero-day Vulnerabilities Patched in September Patch Tuesday Edition
CVE-2026-96951: Windows Shell Security Feature Bypass Vulnerability
A command injection flaw in Windows Shell may allow an unauthenticated attacker to bypass a security feature over a network.
CISA added the vulnerability to its Known Exploited Vulnerabilities Catalog, acknowledging its active exploitation. CISA urged users to patch the vulnerability before October 16, 2026.
CVE-2026-108398: .NET Framework Security Feature Bypass Vulnerability
An untrusted search path flaw in the .NET Framework may allow an authenticated attacker to bypass a security feature locally.
Critical Severity Vulnerabilities Patched in September Patch Tuesday Edition
| CVE | Title | Description |
| CVE-2026-105016 | Microsoft QUIC Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in Microsoft QUIC allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-108471 | Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege Vulnerability | An untrusted pointer dereference flaw in the Windows Virtualization-Based Security (VBS) Enclave allows an authenticated attacker to elevate privileges locally. |
| CVE-2026-108131 | Active Directory Federation Services (AD FS) Spoofing Vulnerability | No CWE for this issue in Active Directory Federation Services (AD FS) allows an unauthenticated attacker to perform spoofing over a network. |
| CVE-2026-108130 | Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Virtualization-Based Security (VBS) Enclave allows an authenticated attacker to elevate privileges locally. |
| CVE-2026-102225 | Windows Text Shaping Remote Code Execution Vulnerability | An out-of-bounds read flaw in Windows Text Shaping allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-102214 | Windows Hyper-V Remote Code Execution Vulnerability | A use-after-free flaw in Windows Hyper-V allows an authenticated attacker to execute code locally. |
| CVE-2026-97814 | Windows Text Shaping Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in Windows Text Shaping allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-100215 | Microsoft Graphics Component Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in the Microsoft Graphics Component allows an unauthenticated attacker to execute code locally. |
| CVE-2026-102211 | Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Virtualization-Based Security (VBS) Enclave allows an authenticated attacker to elevate privileges locally. |
| CVE-2026-100220 | Windows Media Video Decoder Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in the Windows Media Video Decoder allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-100219 | Microsoft QUIC Remote Code Execution Vulnerability | A use-after-free flaw in Microsoft QUIC allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-96913 | Windows Kernel Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Kernel allows an authenticated attacker to elevate privileges locally. |
| CVE-2026-96952 | Microsoft Windows Media Foundation Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in Microsoft Windows Media Foundation allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-100202 | Windows Message Queuing Queue Manager Remote Code Execution Vulnerability | A use-after-free flaw in Windows Message Queuing Queue Manager allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-96202 | Windows Raw Image Extension Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in the Windows Raw Image Extension allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-88207 | Microsoft Office PowerPoint Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in Microsoft Office PowerPoint allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-69802 | Network Device Enrollment Service (NDES) Remote Code Execution Vulnerability | Weak authentication in Network Device Enrollment Service (NDES) allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-70571 | Microsoft Exchange Server Remote Code Execution Vulnerability | A stack-based buffer overflow flaw in Microsoft Exchange Server allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-70250 | Windows DHCP Client Remote Code Execution Vulnerability | A use-after-free flaw in Windows DHCP Client allows an unauthenticated attacker to execute code over an adjacent network. |
| CVE-2026-70229 | Windows Active Directory Domain Services Remote Code Execution Vulnerability | An incorrect authorization flaw in Active Directory Domain Services allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-88174 | Windows Deployment Services Remote Code Execution Vulnerability | A race condition flaw in Windows Deployment Services allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-88171 | Windows DHCP Server Remote Code Execution Vulnerability | A double free flaw in Windows DHCP Server allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-69789 | Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in the Reliable Multicast Transport Driver (RMCAST) allows an unauthenticated attacker to execute code on an adjacent network. |
| CVE-2026-83934 | Windows GDI+ Remote Code Execution Vulnerability | A stack-based buffer overflow flaw in Windows GDI+ allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-62840 | Linux Kernel Elevation of Privilege Vulnerability | A race condition flaw in the Linux Kernel allows an authenticated attacker to elevate privileges locally. |
| CVE-2026-97778 | Microsoft Office Excel Remote Code Execution Vulnerability | An integer overflow or wraparound flaw in Microsoft Office Excel can allow an unauthenticated attacker to execute code over a network. |
| CVE-2026-97739 | Microsoft Office Excel Remote Code Execution Vulnerability | An integer underflow flaw in Microsoft Office Excel allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-97755 | Microsoft Office Excel Remote Code Execution Vulnerability | An out-of-bounds read flaw in Microsoft Office Excel allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-97767 | Microsoft Office Excel Remote Code Execution Vulnerability | A double free flaw in Microsoft Office Excel allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-97749 | Microsoft Office Outlook Remote Code Execution Vulnerability | A double free flaw in Microsoft Office Outlook allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-96943 | Windows Raw Image Extension Remote Code Execution Vulnerability | An integer overflow or wraparound flaw in the Windows Raw Image Extension allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-96222 | Active Directory Federation Services (AD FS) Spoofing Vulnerability | An improper certificate validation flaw in Active Directory Federation Services (AD FS) allows an unauthenticated attacker to perform network spoofing. |
| CVE-2026-88156 | Microsoft Office Outlook Remote Code Execution Vulnerability | A stack-based buffer overflow flaw in Microsoft Office Outlook allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-70300 | Microsoft Office Word Remote Code Execution Vulnerability | Untrusted pointer dereference in Microsoft Office Word allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-88073 | Windows Graphics Kernel Elevation of Privilege Vulnerability | A use-after-free flaw in the Windows Graphics Kernel allows an authenticated attacker to elevate local privileges. |
| CVE-2026-70187 | Windows Remote Desktop Services Remote Code Execution Vulnerability | A use-after-free flaw in Remote Desktop Gateway Service allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-83917 | Windows ALPC Elevation of Privilege Vulnerability | A use-after-free flaw in Windows ALPC allows an authenticated attacker to elevate privileges locally. |
| CVE-2026-105718 | Microsoft Excel Remote Code Execution Vulnerability | An out-of-bounds read flaw in Microsoft Office Excel allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-108400 | HEVC Video Extensions Remote Code Execution Vulnerability | An integer overflow or wraparound flaw in the Microsoft Windows Codecs Library allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-102866 | Microsoft Office SharePoint Elevation of Privilege Vulnerability | An improper verification of a cryptographic signature flaw in Microsoft Office SharePoint allows an unauthenticated attacker to elevate privileges over a network. |
| CVE-2026-105733 | Windows Hyper-V Remote Code Execution Vulnerability | An improper access control flaw in Windows Hyper-V allows an authenticated attacker to execute code locally. |
| CVE-2026-108467 | Microsoft PostScript Printer Driver Remote Code Execution Vulnerability | A heap-based buffer overflow flaw in the Microsoft PostScript Printer Driver allows an authenticated attacker to execute code over a network. |
| CVE-2026-108457 | Microsoft Windows PDF Remote Code Execution Vulnerability | An out-of-bounds write flaw in Microsoft Windows PDF allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-108460 | Windows Message Queuing Remote Code Execution Vulnerability | A use-after-free flaw in Windows Message Queuing allows an unauthenticated attacker to execute code over a network. |
| CVE-2026-108399 | Windows Hyper-V Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows Hyper-V allows an authenticated attacker to elevate privileges locally. |
Microsoft Office PowerPoint Critical Vulnerabilities
| CVE | Description |
| CVE-2026-88144, CVE-2026-70215, CVE-2026-88178 | A use-after-free flaw in Microsoft Office PowerPoint may allow an unauthenticated attacker to execute code over a network. |
Microsoft Office Outlook Critical Vulnerabilities
| CVE | Description |
| CVE-2026-70242, CVE-2026-97016, CVE-2026-70291 | A heap-based buffer overflow flaw in Microsoft Office Outlook may allow an unauthenticated attacker to execute code over a network. |
Microsoft Office Visio Critical Vulnerabilities
| CVE | Description |
| CVE-2026-102857, CVE-2026-102855, CVE-2026-102856 | A heap-based buffer overflow flaw in Microsoft Office Visio may allow an unauthenticated attacker to execute code over a network. |
Windows DHCP Server Critical Vulnerabilities
| CVE | Description |
| CVE-2026-96934, CVE-2026-88117, CVE-2026-88120, CVE-2026-88119 | A use-after-free flaw in Windows DHCP Server may allow an unauthenticated attacker to execute code over a network. |
Microsoft PostScript Printer Driver Critical Vulnerabilities
| CVE | Description |
| CVE-2026-70153, CVE-2026-70147 | A heap-based buffer overflow in the Microsoft PostScript Printer Driver may allow an unauthenticated attacker to execute code over a network. |
Microsoft Office Word Critical Vulnerabilities
| CVE | Description |
| CVE-2026-88185, CVE-2026-70269 | A heap-based buffer overflow flaw in Microsoft Office Word may allow an unauthenticated attacker to execute code over a network. |
Windows Virtualization-Based Security (VBS) Enclave Critical Vulnerabilities
| CVE | Description |
| CVE-2026-96914, CVE-2026-88074 | An integer overflow or wraparound flaw in Windows Virtualization-Based Security (VBS) Enclave may allow an authenticated attacker to elevate privileges locally. |
Microsoft Office Excel Critical Vulnerabilities
| CVE | Description |
| CVE-2026-97756, CVE-2026-100210, CVE-2026-97741, CVE-2026-97765, CVE-2026-97780, CVE-2026-97758, CVE-2026-97776, CVE-2026-97753 | A heap-based buffer overflow flaw in Microsoft Office Excel may allow an unauthenticated attacker to execute code over a network. |
| CVE-2026-100211, CVE-2026-100209, CVE-2026-97745, CVE-2026-97759 | A use-after-free flaw in Microsoft Office Excel may allow an unauthenticated attacker to execute code over a network. |
| CVE-2026-97742, CVE-2026-97761 | A stack-based buffer overflow flaw in Microsoft Office Excel may allow an unauthenticated attacker to execute code over a network. |
Other Microsoft Vulnerability Highlights
| CVE | Title | Description |
| CVE-2026-97798 | Windows Error Reporting Service Elevation of Privilege Vulnerability | Improper neutralization of argument delimiters in a Windows Error Reporting command may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-97799 | Windows Audio Service Elevation of Privilege Vulnerability | An improper verification of a cryptographic signature flaw in the Windows Audio Service may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-102217 | WebDAV Elevation of Privilege Vulnerability | An improper resolution of path equivalence in WebDAV may allow an authenticated attacker to elevate privileges over a network. |
| CVE-2026-100214 | Microsoft Dynamics 365 Business Central Remote Code Execution Vulnerability | Deserialization of untrusted data in Dynamics Business Central may allow an authenticated attacker to execute code over a network. |
| CVE-2026-96939 | Servicing Stack Updates Elevation of Privilege Vulnerability | A race condition flaw in Servicing Stack Updates may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-96929, CVE-2026-83768, CVE-2026-70106 | Windows Kernel Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Kernel may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-96911, CVE-2026-88191, CVE-2026-83704 | Microsoft Windows Search Component Elevation of Privilege Vulnerability | A link-following flaw in the Microsoft Windows Search Component may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-96858 | Windows Security Account Manager Tampering Vulnerability | Missing authentication for a critical function in the Windows Security Account Manager may allow an authenticated attacker to perform local tampering. |
| CVE-2026-70279 | Microsoft Exchange Server Spoofing Vulnerability | A cross-site scripting flaw in Microsoft Exchange Server may allow an unauthenticated attacker to perform network-based spoofing. |
| CVE-2026-88093, CVE-2026-70255 | Desktop Window Manager Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Desktop Window Manager may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70571 | Microsoft Exchange Server Remote Code Execution Vulnerability | A stack-based buffer overflow flaw in Microsoft Exchange Server may allow an unauthenticated attacker to execute code over a network. |
| CVE-2026-70054 | Windows NetBIOS Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows NetBIOS may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-88133 | Windows Portable Device Enumerator Service Elevation of Privilege Vulnerability | An improper authorization in the Windows Portable Device Enumerator Service may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-88152 | Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege Vulnerability | A use-after-free flaw in the Windows Background Intelligent Transfer Service (BITS) may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-88147 | Windows Secure Socket Tunneling Protocol (SSTP) Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Secure Sockets Tunneling Protocol (SSTP) may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-88118 | Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege Vulnerability | An integer overflow or wraparound flaw in the Windows Background Intelligent Transfer Service (BITS) may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-85941 | Windows Installer Elevation of Privilege Vulnerability | A race condition flaw in Windows Installer may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-85884 | Windows Health and Optimized Experiences Service Elevation of Privilege Vulnerability | Missing authentication for a critical function in the Windows Health and Optimized Experiences Service could allow an authenticated attacker to elevate local privileges. |
| CVE-2026-85908, CVE-2026-85901, CVE-2026-70286 | Windows Graphics Component Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows Win32K – GRFX may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-85906, CVE-2026-70151 | Windows Direct Composition Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Direct Composition may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-85902, CVE-2026-83896, CVE-2026-83902 | Windows Direct Composition Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows Direct Composition may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83899 | Windows Installer Elevation of Privilege Vulnerability | An improper privilege management flaw in Windows Installer may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83840 | Windows Error Reporting Elevation of Privilege Vulnerability | Weak authentication flaw in Windows Error Reporting may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83830 | Windows COM+ Event System Service Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows COM+ Event System Service may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-83750 | Windows Error Reporting Elevation of Privilege Vulnerability | A race condition in Windows Error Reporting may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83735, CVE-2026-85850 | Windows Kernel Elevation of Privilege Vulnerability | Release of an invalid pointer or reference in the Windows Kernel may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83732 | Win32k Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Win32K could allow an authenticated attacker to elevate local privileges. |
| CVE-2026-69733, CVE-2026-69882 | Windows Update Elevation of Privilege Vulnerability | Untrusted search path in Windows Update may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83785 | Windows COM+ Event System Service Elevation of Privilege Vulnerability | A use-after-free flaw in the Windows COM+ Event System Service may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-83717 | Windows Installer Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Installer may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70144, CVE-2026-70236, CVE-2026-70271, CVE-2026-70273, CVE-2026-70253, CVE-2026-70249, CVE-2026-70176, CVE-2026-70076 | Windows Win32k Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Win32 Kernel Subsystem may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83763 | Windows Input System Elevation of Privilege Vulnerability | A type confusion flaw in the Windows Input System may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83724 | Windows Management Instrumentation Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows Management Instrumentation may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-81971 | Windows NTFS Elevation of Privilege Vulnerability | A race condition flaw in Windows NTFS may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83509 | Windows Setup Files Cleanup Elevation of Privilege Vulnerability | Untrusted search path in Windows Setup Files Cleanup may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-69783 | Windows Update Elevation of Privilege Vulnerability | External control of the file name or path in Windows Update may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-83505, CVE-2026-83510 | Windows Setup Files Cleanup Elevation of Privilege Vulnerability | A race condition flaw in Windows Setup Files Cleanup may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70237, CVE-2026-83738 | Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability | A use-after-free flaw in the Windows Ancillary Function Driver for WinSock may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-69880, CVE-2026-69926 | Desktop Window Manager Elevation of Privilege Vulnerability | A type confusion flaw in the Desktop Window Manager may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-69452 | Windows Enterprise App Management Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Enterprise App Management may allow an authenticated attacker to elevate privileges over a network. |
| CVE-2026-69923 | Windows AI Elevation of Privilege Vulnerability | AN uncontrolled search path element in Windows AI may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-85855 | Windows DWM Core Library Elevation of Privilege Vulnerability | A use-after-free flaw in Windows DWM Core Library may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-88159 | Windows Background Intelligent Transfer Service (BITS) Remote Code Execution Vulnerability | A use-after-free flaw in Windows Background Intelligent Transfer Service (BITS) may allow an unauthenticated attacker to execute code over a network. |
| CVE-2026-85848, CVE-2026-85832 | Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Background Intelligent Transfer Service (BITS) may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-85945 | Windows Kernel Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Kernel may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70303 | Windows Kernel Elevation of Privilege Vulnerability | An out-of-bounds write flaw in the Windows Kernel may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-85870, CVE-2026-70233 | Windows Common Log File System Driver Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows Common Log File System Driver may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-85849 | Windows AppX Deployment Service Elevation of Privilege Vulnerability | A link-following flaw in the Windows AppX Deployment Service may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-85843 | Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege Vulnerability | Use of an uninitialized resource in the Windows Background Intelligent Transfer Service (BITS) may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-85791 | Windows Encrypting File System (EFS) Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Encrypting File System (EFS) may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-83793 | Windows Update Orchestrator Service Elevation of Privilege Vulnerability | A link-following flaw in the Windows Update Orchestrator Service may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-85804, CVE-2026-85802, CVE-2026-83761 | Windows Win32 Kernel Subsystem Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Win32 Kernel Subsystem may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70241 | Windows Kerberos Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Kerberos may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-84014 | Windows Device Association Service Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Device Association Service may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-85355 | Windows Common Log File System Driver Elevation of Privilege Vulnerability | Inclusion of functionality from an untrusted control sphere in the Windows Common Log File System Driver may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83921 | Windows Search Service Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Microsoft Windows Search Component may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-83769 | Microsoft OpenSSH for Windows Elevation of Privilege Vulnerability | A use-after-free flaw in OpenSSH for Windows may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83927 | Windows Registry Elevation of Privilege Vulnerability | A link-following flaw in the Windows Registry may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-83834 | Windows Kernel-Mode Drivers Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Kernel-Mode Drivers may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83886 | Windows Update Orchestrator Service Elevation of Privilege Vulnerability | A use-after-free flaw in the Windows Update Orchestrator Service may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-83867 | Windows Push Notifications Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows Push Notifications may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83848 | Windows COM+ Event System Service Elevation of Privilege Vulnerability | An untrusted pointer dereference in the Windows COM+ Event System Service may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83842 | Windows TCP/IP Elevation of Privilege Vulnerability | Double free in Windows TCP/IP may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83699 | Windows Client-Side Caching (CSC) Service Elevation of Privilege Vulnerability | A stack-based buffer overflow flaw in the Windows Client-Side Caching (CSC) Service may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-83669 | Windows Error Reporting Elevation of Privilege Vulnerability | Use of uninitialized resource in Windows Error Reporting may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-83580 | Windows Client-Side Caching (CSC) Service Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Client-Side Caching (CSC) Service may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-69673 | Windows Update Elevation of Privilege Vulnerability | A link-following flaw in Windows Update may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-69718 | Windows Update Elevation of Privilege Vulnerability | A command injection flaw in Windows Update may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-72955 | Windows Application Compatibility Cache Elevation of Privilege Vulnerability | A use-after-free flaw in the Windows Application Compatibility Cache may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-70223 | Windows Console Driver Elevation of Privilege Vulnerability | A use-after-free flaw in Windows Console Driver may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70218 | Windows StateRepository API Elevation of Privilege Vulnerability | Insufficient granularity of access control in Windows StateRepository API may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70245 | Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability | A type confusion flaw in Windows Ancillary Function Driver for WinSock may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70156 | Microsoft Windows Search Component Elevation of Privilege Vulnerability | A use-after-free flaw in Microsoft Windows Search Component may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70132 | Windows Portable Device File System Driver Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Portable Device File System Driver may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70108, CVE-2026-70117, CVE-2026-70060 | Windows Win32k Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in the Windows Win32 Kernel Subsystem may allow an authenticated attacker to elevate local privileges. |
| CVE-2026-70103 | Windows Error Reporting Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows Error Reporting may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-70104 | Windows Win32k Elevation of Privilege Vulnerability | An untrusted pointer dereference in the Windows Win32 Kernel Subsystem may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-69918 | Windows Core Messaging Elevation of Privilege Vulnerability | A heap-based buffer overflow flaw in Windows Core Messaging may allow an authenticated attacker to elevate privileges locally. |
| CVE-2026-97800 | Windows Mobile Broadband Elevation of Privilege Vulnerability | An incorrect permission assignment for a critical resource in Windows Mobile Broadband may allow an authenticated attacker to elevate privileges locally. |
Microsoft Release Summary
This month’s security updates cover the following Microsoft product families:
| Product Family | Vulnerabilities | Distinct Updates |
| Windows | 1102 | 39 |
| Office | 134 | 11 |
| SharePoint Server | 36 | 1 |
| SQL Server | 22 | 8 |
| Exchange Server | 7 | 8 |
| Developer Tools (Dev Div) | 61 | 60 |
| Azure | 15 | 20 |
| Defender | 4 | 3 |
| Edge | 0 | 1 |
| Other | 32 | 25 |
| Total | 1414 | 176 |
Discover and Prioritize Vulnerabilities in Vulnerability Management, Detection & Response (VMDR)
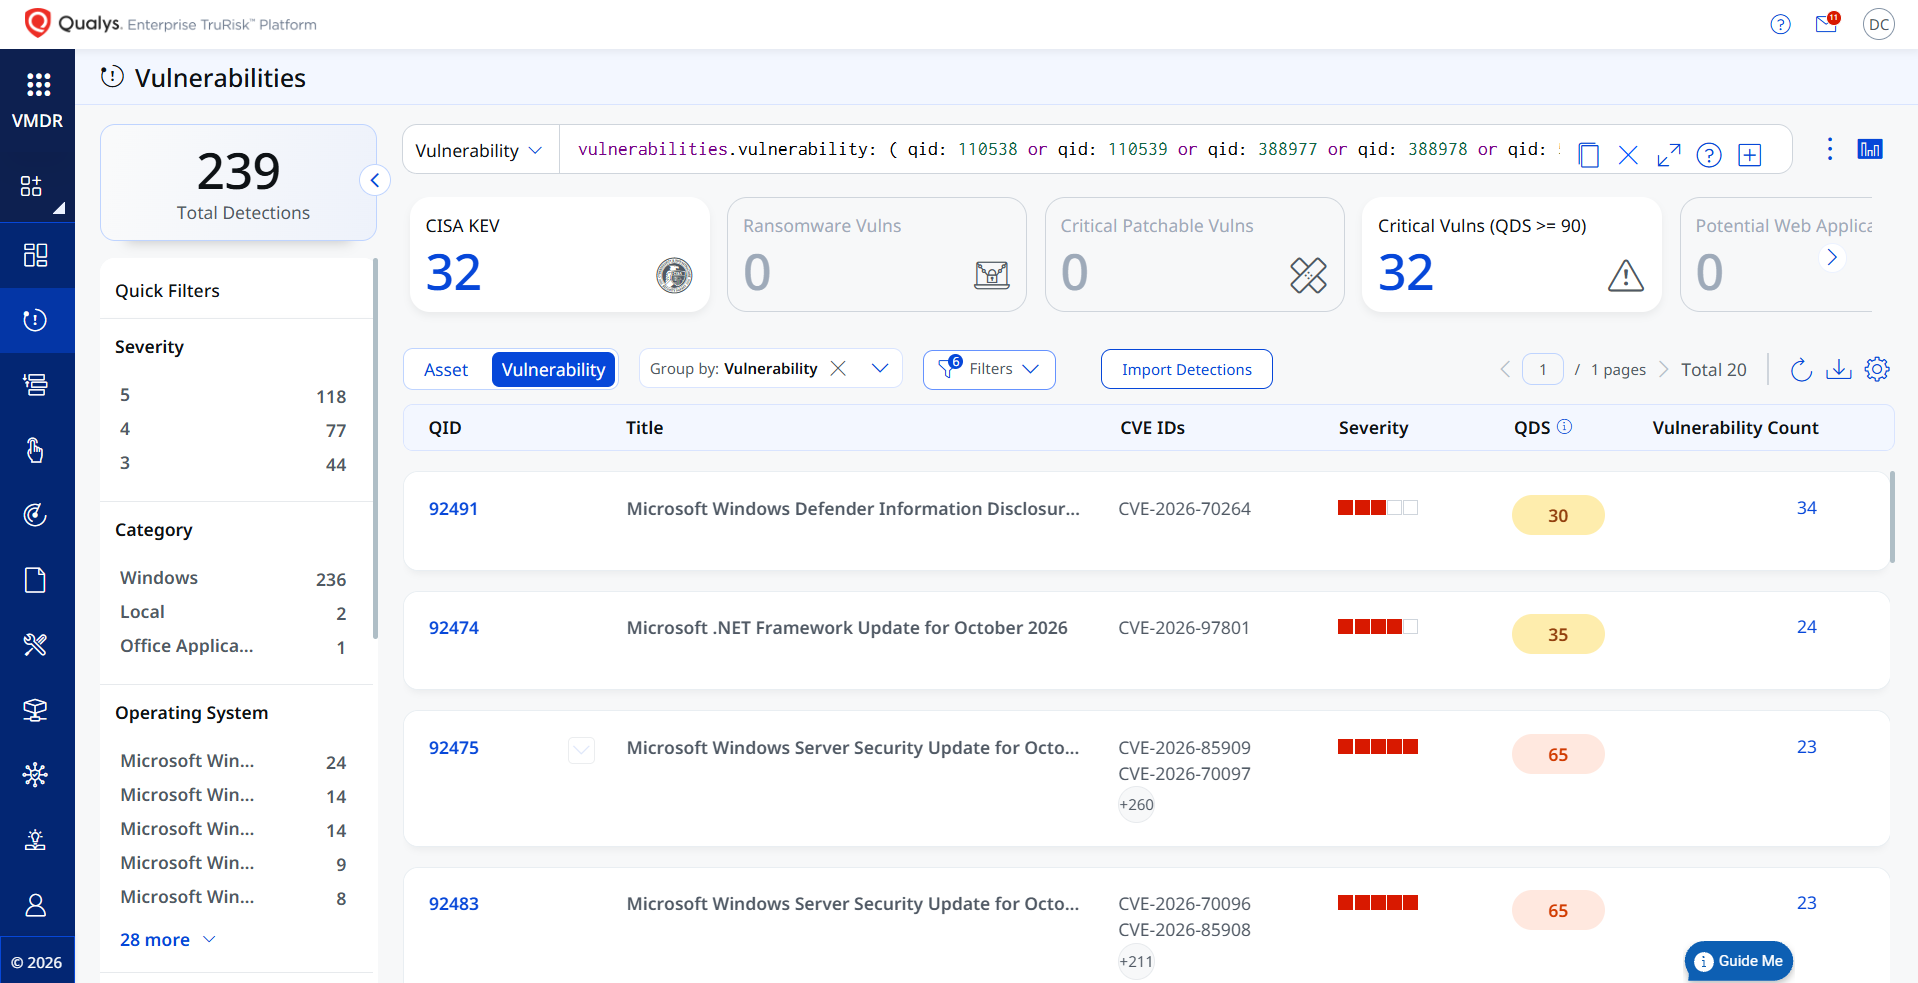
Qualys VMDR automatically detects new Patch Tuesday vulnerabilities using continuous updates to its Knowledgebase (KB).
You can see all your impacted hosts by these vulnerabilities using the following QQL query:
vulnerabilities.vulnerability: ( qid: 110538 or qid: 110539 or qid: 388977 or qid: 388978 or qid: 50152 or qid: 92473 or qid: 92474 or qid: 92475 or qid: 92476 or qid: 92477 or qid: 92478 or qid: 92479 or qid: 92480 or qid: 92481 or qid: 92482 or qid: 92483 or qid: 92484 or qid: 92485 or qid: 92486 or qid: 92487 or qid: 92488 or qid: 92489 or qid: 92490 or qid: 92491 or qid: 92492 or qid: 92493 or qid: 92494 or qid: 92495 )
Rapid Response with TruRisk™ Eliminate
Patch to the Latest Version
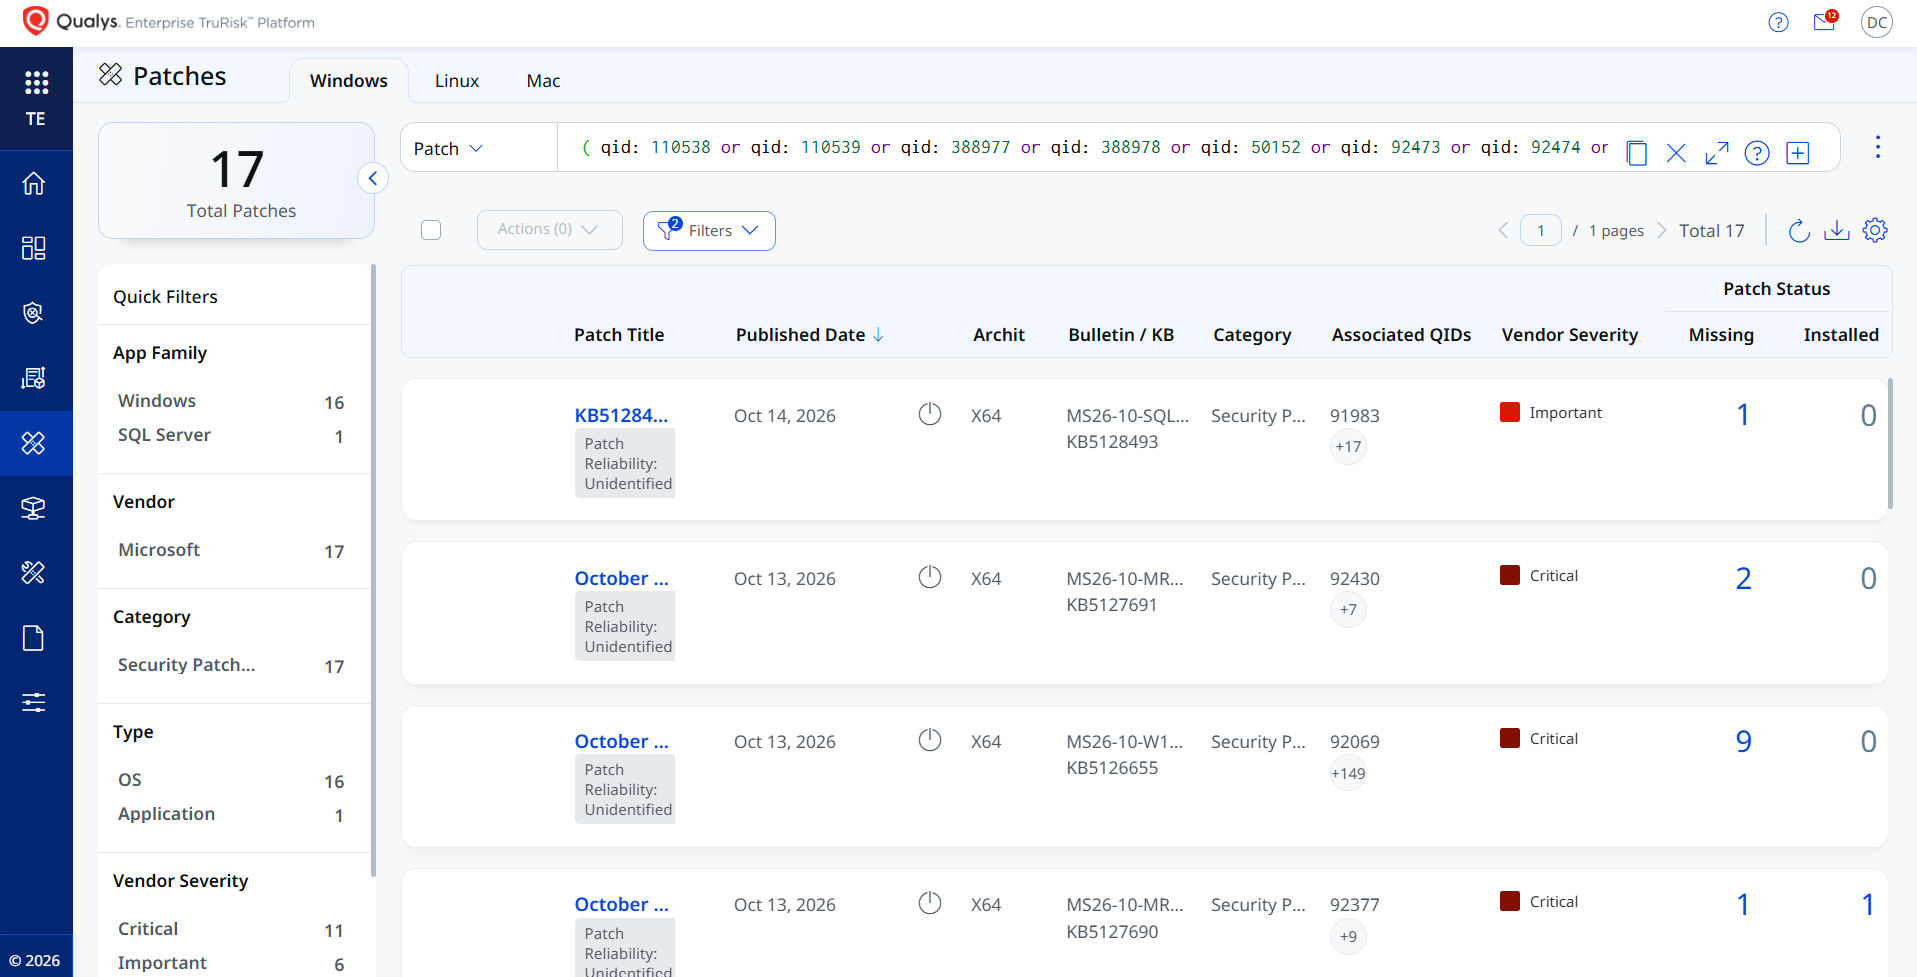
VMDR rapidly remediates Windows hosts by deploying the most relevant and applicable per-technology version patches. You can simply select the respective QIDs in the Patch Catalog and filter for “Missing” patches to identify and deploy the applicable, available patches with one click.
The following QQL will return the missing patches for this Patch Tuesday:
( qid: 110538 or qid: 110539 or qid: 388977 or qid: 388978 or qid: 50152 or qid: 92473 or qid: 92474 or qid: 92475 or qid: 92476 or qid: 92477 or qid: 92478 or qid: 92479 or qid: 92480 or qid: 92481 or qid: 92482 or qid: 92483 or qid: 92484 or qid: 92485 or qid: 92486 or qid: 92487 or qid: 92488 or qid: 92489 or qid: 92490 or qid: 92491 or qid: 92492 or qid: 92493 or qid: 92494 or qid: 92495 )
Mitigation: Reducing Risk Until Remediation
As a first set of our mitigant signature set, we have Qualys-created mitigations for the following 608 vulnerabilities: CVE-2026-83846, CVE-2026-95943, CVE-2026-83868, CVE-2026-83776, CVE-2026-96844, CVE-2026-83760, CVE-2026-88158, CVE-2026-87692, CVE-2026-77910, CVE-2026-87696, CVE-2026-70571, CVE-2026-70279, CVE-2026-96940, CVE-2026-87695, CVE-2026-88196, CVE-2026-88197, CVE-2026-105596, CVE-2026-105595, CVE-2026-102849, CVE-2026-102850, CVE-2026-105716, CVE-2026-105714, CVE-2026-105593, CVE-2026-105598, CVE-2026-105592, CVE-2026-94506, CVE-2026-105597, CVE-2026-105591, CVE-2026-70276, CVE-2026-97774, CVE-2026-88109, CVE-2026-85340, CVE-2026-88201, CVE-2026-88190, CVE-2026-88184, CVE-2026-88192, CVE-2026-88195, CVE-2026-100211, CVE-2026-97766, CVE-2026-97780, CVE-2026-97767, CVE-2026-97775, CVE-2026-97779, CVE-2026-100212, CVE-2026-97752, CVE-2026-88145, CVE-2026-88151, CVE-2026-97773, CVE-2026-88153, CVE-2026-88154, CVE-2026-97768, CVE-2026-97769, CVE-2026-100210, CVE-2026-88175, CVE-2026-88172, CVE-2026-100209, CVE-2026-97770, CVE-2026-97771, CVE-2026-97772, CVE-2026-97778, CVE-2026-97776, CVE-2026-97777, CVE-2026-69922, CVE-2026-97742, CVE-2026-70219, CVE-2026-97745, CVE-2026-97738, CVE-2026-97003, CVE-2026-77902, CVE-2026-70254, CVE-2026-97743, CVE-2026-97741, CVE-2026-97763, CVE-2026-97762, CVE-2026-97017, CVE-2026-97761, CVE-2026-97759, CVE-2026-97758, CVE-2026-97757, CVE-2026-97756, CVE-2026-97755, CVE-2026-97754, CVE-2026-97765, CVE-2026-97753, CVE-2026-97760, CVE-2026-97011, CVE-2026-97004, CVE-2026-97739, CVE-2026-97007, CVE-2026-97008, CVE-2026-97014, CVE-2026-97746, CVE-2026-97751, CVE-2026-97750, CVE-2026-97747, CVE-2026-70214, CVE-2026-97740, CVE-2026-97009, CVE-2026-97010, CVE-2026-97748, CVE-2026-102858, CVE-2026-97781, CVE-2026-96997, CVE-2026-70281, CVE-2026-70282, CVE-2026-70291, CVE-2026-97749, CVE-2026-88156, CVE-2026-70256, CVE-2026-97016, CVE-2026-70257, CVE-2026-70242, CVE-2026-97012, CVE-2026-88144, CVE-2026-88207, CVE-2026-97744, CVE-2026-105599, CVE-2026-97005, CVE-2026-88183, CVE-2026-88178, CVE-2026-70215, CVE-2026-88203, CVE-2026-70298, CVE-2026-85900, CVE-2026-88200, CVE-2026-88198, CVE-2026-70251, CVE-2026-70217, CVE-2026-70267, CVE-2026-70266, CVE-2026-88166, CVE-2026-88163, CVE-2026-70246, CVE-2026-70202, CVE-2026-88155, CVE-2026-85932, CVE-2026-70259, CVE-2026-102865, CVE-2026-102859, CVE-2026-102860, CVE-2026-102861, CVE-2026-69943, CVE-2026-102864, CVE-2026-97782, CVE-2026-102866, CVE-2026-97783, CVE-2026-102863, CVE-2026-88208, CVE-2026-96044, CVE-2026-88204, CVE-2026-88206, CVE-2026-105713, CVE-2026-88209, CVE-2026-102862, CVE-2026-105720, CVE-2026-105013, CVE-2026-102855, CVE-2026-102856, CVE-2026-102857, CVE-2026-70268, CVE-2026-102867, CVE-2026-88202, CVE-2026-70269, CVE-2026-70220, CVE-2026-88210, CVE-2026-70302, CVE-2026-70301, CVE-2026-70300, CVE-2026-88185, CVE-2026-88186, CVE-2026-88167, CVE-2026-88169, CVE-2026-96996, CVE-2026-96995, CVE-2026-83891, CVE-2026-70287, CVE-2026-105715, CVE-2026-97001, CVE-2026-70263, CVE-2026-88150, CVE-2026-70206, CVE-2026-70110, CVE-2026-70109, CVE-2026-70153, CVE-2026-70147, CVE-2026-70092, CVE-2026-102199, CVE-2026-96911, CVE-2026-96910, CVE-2026-70177, CVE-2026-70173, CVE-2026-96324, CVE-2026-70150, CVE-2026-70156, CVE-2026-85869, CVE-2026-96937, CVE-2026-105010, CVE-2026-83570, CVE-2026-83564, CVE-2026-83920, CVE-2026-83921, CVE-2026-70141, CVE-2026-83575, CVE-2026-83829, CVE-2026-83574, CVE-2026-83850, CVE-2026-70086, CVE-2026-83686, CVE-2026-83725, CVE-2026-83704, CVE-2026-88182, CVE-2026-88191, CVE-2026-88160, CVE-2026-70136, CVE-2026-70115, CVE-2026-83769, CVE-2026-83754, CVE-2026-70163, CVE-2026-83871, CVE-2026-83923, CVE-2026-88157, CVE-2026-69977, CVE-2026-69789, CVE-2026-85943, CVE-2026-103575, CVE-2026-69998, CVE-2026-69997, CVE-2026-97789, CVE-2026-69988, CVE-2026-85337, CVE-2026-70004, CVE-2026-69995, CVE-2026-69994, CVE-2026-69991, CVE-2026-70012, CVE-2026-83688, CVE-2026-69984, CVE-2026-69986, CVE-2026-69987, CVE-2026-70006, CVE-2026-69976, CVE-2026-69996, CVE-2026-70033, CVE-2026-100218, CVE-2026-84007, CVE-2026-84012, CVE-2026-70187, CVE-2026-103560, CVE-2026-83642, CVE-2026-88129, CVE-2026-88130, CVE-2026-88112, CVE-2026-88116, CVE-2026-83889, CVE-2026-88122, CVE-2026-96926, CVE-2026-88123, CVE-2026-70087, CVE-2026-83869, CVE-2026-70085, CVE-2026-85903, CVE-2026-70071, CVE-2026-70083, CVE-2026-70127, CVE-2026-70167, CVE-2026-70244, CVE-2026-83635, CVE-2026-88125, CVE-2026-88114, CVE-2026-85370, CVE-2026-87714, CVE-2026-70262, CVE-2026-88137, CVE-2026-85828, CVE-2026-85827, CVE-2026-88136, CVE-2026-96843, CVE-2026-88135, CVE-2026-88126, CVE-2026-96846, CVE-2026-96847, CVE-2026-102217, CVE-2026-69945, CVE-2026-69914, CVE-2026-85849, CVE-2026-69979, CVE-2026-69969, CVE-2026-85934, CVE-2026-69905, CVE-2026-83571, CVE-2026-70118, CVE-2026-96314, CVE-2026-83644, CVE-2026-70140, CVE-2026-70230, CVE-2026-85843, CVE-2026-88142, CVE-2026-85848, CVE-2026-88121, CVE-2026-88118, CVE-2026-88146, CVE-2026-88152, CVE-2026-88159, CVE-2026-88173, CVE-2026-85832, CVE-2026-70184, CVE-2026-62687, CVE-2026-85831, CVE-2026-83827, CVE-2026-87713, CVE-2026-70126, CVE-2026-83739, CVE-2026-83777, CVE-2026-85377, CVE-2026-83888, CVE-2026-70041, CVE-2026-70275, CVE-2026-70270, CVE-2026-97787, CVE-2026-97792, CVE-2026-97790, CVE-2026-97794, CVE-2026-102202, CVE-2026-88174, CVE-2026-85342, CVE-2026-85352, CVE-2026-83710, CVE-2026-96854, CVE-2026-85332, CVE-2026-85815, CVE-2026-85904, CVE-2026-70227, CVE-2026-85331, CVE-2026-85336, CVE-2026-84014, CVE-2026-70082, CVE-2026-70119, CVE-2026-70079, CVE-2026-70074, CVE-2026-70166, CVE-2026-70155, CVE-2026-88180, CVE-2026-88194, CVE-2026-88181, CVE-2026-83765, CVE-2026-85855, CVE-2026-88188, CVE-2026-83726, CVE-2026-88179, CVE-2026-88177, CVE-2026-85853, CVE-2026-85854, CVE-2026-88189, CVE-2026-88128, CVE-2026-83826, CVE-2026-83658, CVE-2026-83693, CVE-2026-83747, CVE-2026-83689, CVE-2026-83519, CVE-2026-69363, CVE-2026-83748, CVE-2026-83750, CVE-2026-83669, CVE-2026-83643, CVE-2026-83916, CVE-2026-70103, CVE-2026-83758, CVE-2026-83715, CVE-2026-85800, CVE-2026-69387, CVE-2026-85354, CVE-2026-69354, CVE-2026-83840, CVE-2026-83926, CVE-2026-83849, CVE-2026-83853, CVE-2026-83907, CVE-2026-83740, CVE-2026-70280, CVE-2026-83790, CVE-2026-83705, CVE-2026-83714, CVE-2026-70247, CVE-2026-70208, CVE-2026-96223, CVE-2026-83766, CVE-2026-85369, CVE-2026-88071, CVE-2026-83671, CVE-2026-70023, CVE-2026-83728, CVE-2026-105733, CVE-2026-83636, CVE-2026-70248, CVE-2026-83839, CVE-2026-102214, CVE-2026-85343, CVE-2026-83931, CVE-2026-87705, CVE-2026-83716, CVE-2026-83523, CVE-2026-85842, CVE-2026-85930, CVE-2026-69705, CVE-2026-69883, CVE-2026-69644, CVE-2026-69721, CVE-2026-70095, CVE-2026-69521, CVE-2026-70013, CVE-2026-70031, CVE-2026-70038, CVE-2026-69634, CVE-2026-96921, CVE-2026-85334, CVE-2026-85874, CVE-2026-85860, CVE-2026-100202, CVE-2026-85859, CVE-2026-83828, CVE-2026-83751, CVE-2026-83773, CVE-2026-88079, CVE-2026-84018, CVE-2026-83733, CVE-2026-85320, CVE-2026-85327, CVE-2026-85376, CVE-2026-85847, CVE-2026-85933, CVE-2026-85353, CVE-2026-69596, CVE-2026-72934, CVE-2026-83781, CVE-2026-72969, CVE-2026-72968, CVE-2026-96920, CVE-2026-69743, CVE-2026-85328, CVE-2026-70084, CVE-2026-96857, CVE-2026-84009, CVE-2026-70198, CVE-2026-83867, CVE-2026-96313, CVE-2026-85867, CVE-2026-70137, CVE-2026-87698, CVE-2026-59116, CVE-2026-83861, CVE-2026-96322, CVE-2026-102198, CVE-2026-69992, CVE-2026-70048, CVE-2026-70116, CVE-2026-83586, CVE-2026-96245, CVE-2026-96316, CVE-2026-85792, CVE-2026-84020, CVE-2026-84017, CVE-2026-85339, CVE-2026-70158, CVE-2026-85794, CVE-2026-103558, CVE-2026-85808, CVE-2026-70057, CVE-2026-85322, CVE-2026-85809, CVE-2026-88147, CVE-2026-85926, CVE-2026-81969, CVE-2026-83499, CVE-2026-105009, CVE-2026-83789, CVE-2026-84011, CVE-2026-70133, CVE-2026-96325, CVE-2026-88127, CVE-2026-70027, CVE-2026-85879, CVE-2026-96309, CVE-2026-96206, CVE-2026-84013, CVE-2026-85810, CVE-2026-83857, CVE-2026-83713, CVE-2026-102205, CVE-2026-85909, CVE-2026-85820, CVE-2026-83513, CVE-2026-102218, CVE-2026-96930, CVE-2026-96953, CVE-2026-96946, CVE-2026-96947, CVE-2026-96949, CVE-2026-96950, CVE-2026-85821, CVE-2026-85825, CVE-2026-102215, CVE-2026-85373, CVE-2026-85918, CVE-2026-85927, CVE-2026-85375, CVE-2026-83638, CVE-2026-83588, CVE-2026-85935, CVE-2026-96301, CVE-2026-96250, CVE-2026-96319, CVE-2026-96253, CVE-2026-96254, CVE-2026-96304, CVE-2026-96310, CVE-2026-96860, CVE-2026-85807, CVE-2026-85341, CVE-2026-96243, CVE-2026-70045, CVE-2026-103569, CVE-2026-83795, CVE-2026-83685, CVE-2026-83522, CVE-2026-83521, CVE-2026-84015, CVE-2026-103565, CVE-2026-85938, CVE-2026-102195, CVE-2026-102196, CVE-2026-96919, CVE-2026-70148, CVE-2026-70122, CVE-2026-103567, CVE-2026-88103, CVE-2026-88105, CVE-2026-88113, CVE-2026-103554, CVE-2026-102193, CVE-2026-105722, CVE-2026-102197, CVE-2026-96948, CVE-2026-70149, CVE-2026-70068, CVE-2026-83698, CVE-2026-83699, CVE-2026-83580, CVE-2026-83701, CVE-2026-83700, CVE-2026-83844, CVE-2026-70113, CVE-2026-69955, CVE-2026-69940, CVE-2026-69949, CVE-2026-69675, CVE-2026-102186, CVE-2026-70143, CVE-2026-96209, CVE-2026-88133, CVE-2026-83664, CVE-2026-70132, CVE-2026-83794, CVE-2026-102206, CVE-2026-83565, CVE-2026-88162, CVE-2026-83759, CVE-2026-83784, CVE-2026-85791, CVE-2026-83683, CVE-2026-87707, CVE-2026-70142, CVE-2026-70139, CVE-2026-100203, CVE-2026-70056, CVE-2026-100200, CVE-2026-69733, CVE-2026-69633, CVE-2026-96323, CVE-2026-69783, CVE-2026-69673, CVE-2026-69882, CVE-2026-69718, CVE-2026-69999, CVE-2026-85357, CVE-2026-83886, CVE-2026-83933, CVE-2026-81964, CVE-2026-83930, CVE-2026-83507, CVE-2026-83793, CVE-2026-83753, CVE-2026-85803, CVE-2026-83771, CVE-2026-96183, CVE-2026-83639, CVE-2026-83854, CVE-2026-96923, CVE-2026-83855, CVE-2026-83668, CVE-2026-69798, CVE-2026-85829, CVE-2026-85816, CVE-2026-83703, CVE-2026-96951, CVE-2026-88106, CVE-2026-88107, CVE-2026-83696.
For vulnerabilities in Windows services with local or remote exploitation vectors, our mitigations modify configuration by altering registry keys and, where applicable, service policy files. These mitigations work for affected components such as the Connected Devices Platform Service (Cdpsvc), Bluetooth / Port Driver, Digest Authentication, PostScript Printer Driver, Codecs Library, Search Component, OpenSSH for Windows, Quality Windows Audio/Video Experience (QWAVE) service, Reliable Multicast Transport Driver (RMCAST), Remote Desktop Client, Remote Desktop Gateway Service, Remote Desktop Services, DNS Server, WebDAV, AppX Deployment Extensions, Audio Service, Background Intelligent Transfer Service (BITS), Backup Engine, Biometric Service, CD-ROM Driver, Container Isolation FS Filter Driver, Deployment Services, Device Association Service, DWM Core Library, Error Reporting, Windows Hello, HTTP.sys, Hyper-V, Image Acquisition, iSCSI, Message Queuing Queue Manager, MIDI Service, Print Spooler, Program Compatibility Assistant Service, Projected File System, Push Notifications, Remote Access Connection Manager, Resilient File System (ReFS), Routing and Remote Access Service (RRAS), Secure Socket Tunneling Protocol (SSTP), Server Update Service (WSUS), SMB Client, SMB Server, Subsystem for Linux, Telephony Server, Universal Disk Format File System Driver (UDFS), Universal Plug and Play (UPnP) Device Host, USB Driver, USB Print Driver, USB Video Driver, WalletService, Work Folders, Internet Key Exchange (IKE) Extension, Remote Access Point-to-Point Protocol (PPP) EAP-TLS, Broadcast DVR User Service, Client Side Caching driver (csc.sys), Now Playing Session Manager, Paint, Client for NFS, Network File System, Portable Device Enumerator Service, Encrypting File System (EFS), Fax and Scan Service, Update Service, Phone Service, Update Orchestrator Service, Camera Frame Server Monitor, Health and Optimized Experiences Service, Sensor Data Service, Notification, Workstation Service, WLAN Service, Wired AutoConfig Service, Wi-Fi Driver, Shell, and Cloud Files Mini Filter Driver, as well as Microsoft Office applications (Word, Excel, PowerPoint, OneNote, Outlook, Access, Visio, and Click-to-Run), Microsoft SharePoint Server, and Microsoft Exchange Server.
Additionally, this mitigation set addresses remote code execution, elevation of privilege, information disclosure, denial-of-service, spoofing, tampering, and security feature bypass risks across these components.
Qualys TruRisk Mitigate product customers receive these scripts as part of the monthly Patch Tuesday signature set.
The next Patch Tuesday is scheduled for November 10, and we will provide details and patch analysis then. Until next Patch Tuesday, stay safe and secure. Be sure to subscribe to the ‘This Month in Vulnerabilities and Patches’ webinar.’
Qualys Monthly Webinar Series
The Qualys Research team hosts a monthly webinar series to help our existing customers leverage the seamless integration between Qualys Vulnerability Management, Detection & Response (VMDR), and Qualys TruRisk Eliminate. Combining these two solutions can reduce the median time to remediate critical vulnerabilities.
During the webcast, we will discuss this month’s high-impact vulnerabilities, including those highlighted in this month’s Patch Tuesday alert. We will walk you through the necessary steps to address the key vulnerabilities using Qualys VMDR and Qualys TruRisk Eliminate.
Join the webinar
This Month in Vulnerabilities & Patches